duokey
Multi-Party Computation (MPC) Key Management & Post-Quantum Cryptography
Swiss private banking cryptographic enclave securing sovereign data vaults with Multi-Party Computation, zero-knowledge attestation, and hardware security module orchestration across multi-cloud infrastructure.
Zero plain-text key exposure in memory or at rest
Sub-millisecond mathematical shard derivation
Hardware Security Module (HSM) cluster attestation
Swiss Federal Data Protection Act & GDPR Art. 32
Swiss private wealth managers and international banking groups faced severe regulatory barriers when transitioning customer records and transaction vaults to the public cloud. Under FINMA circulars and the Swiss Federal Act on Data Protection (FADP), banks are legally prohibited from granting third-party hypervisors or foreign cloud providers access to decryption keys.
Traditional Hardware Security Modules (HSMs) created rigid operational silos and required weeks of manual ceremonies for key rotation. If a cloud provider was subpoenaed under the US CLOUD Act, traditional encryption provided zero legal defense because the cloud host held master encryption keys in memory.
Core Workstreams Executed:
- Engineered a Multi-Party Computation (MPC) key management architecture using Shamir's threshold secret sharing protocols.
- Deployed isolated AWS Nitro Enclaves and Thales Luna HSM clusters to guarantee zero plain-text key storage.
- Integrated post-quantum cryptographic primitives (ML-KEM / ML-DSA) to future-proof banking assets against quantum cryptanalysis.
- Established continuous remote attestation protocols and deterministic tamper-proof audit nonces for FINMA regulatory inspections.
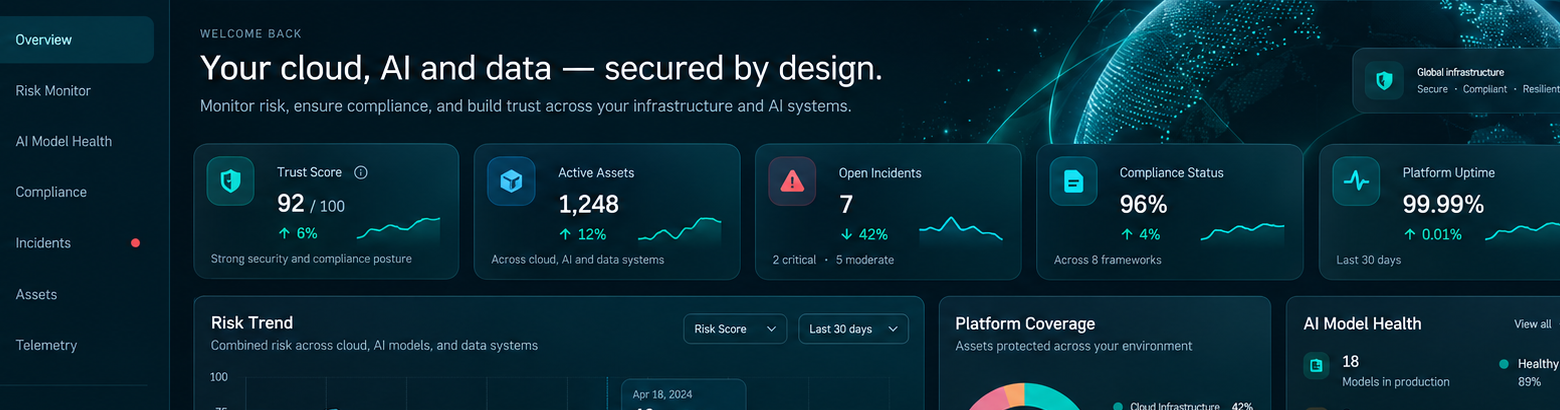
Cryptographic Enclave Health & Key Governance Telemetry
The sovereign security control center provides real-time cryptographic telemetry. Security officers can monitor active MPC key shards, hardware tamper sensors, and enclave attestation status across global data centers.
- check_circle Continuous verification of 2.8M active cryptographic keys across independent jurisdictions
- check_circle Real-time hardware tamper detection with instant cryptographic key self-destruction circuits
- check_circle Sub-10ms cryptographic operation speeds handling over 14,000 signature requests per second
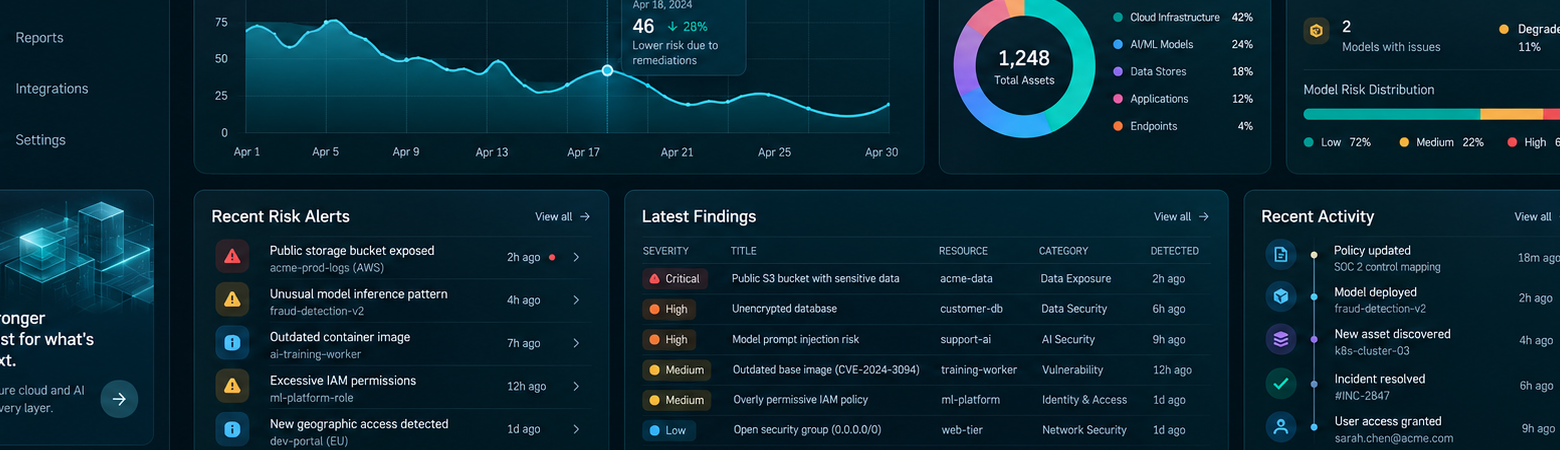
Multi-Cloud Attestation Status & Audit Nonce Ledger
A microscopic view into the enclave attestation verification engine. Every cryptographic request must pass remote cryptographic hardware attestation before key shares participate in computation.
- check_circle Real-time validation of cryptographic measurement hashes (PCR registers) on AMD SEV and AWS Nitro
- check_circle Automated zero-downtime key rotation executed every 24 hours without service disruption
- check_circle Cryptographic proof-of-custody nonces exported directly for external FINMA and SOC-2 auditors
Our cryptography engineers deployed an MPC threshold scheme where the private key is never assembled in a single location. Instead, mathematical key shares are distributed across three distinct legal jurisdictions: on-premises bank HSMs, a Swiss sovereign cloud enclave, and the client's public cloud tenant.
When a decryption or signature operation is requested, cryptographic co-processors perform a secure multi-party computation protocol. The message is decrypted or signed without ever reconstructing the private key in plaintext memory, mathematically neutralizing cloud host compromises.
Core Production Stack:
7-Stage DAG Architecture Blueprint
Live signal pulses tracing data ingress through classification, parallel branches, and persistent storage
Measurable Impact & Concrete Business Returns
Every line of code delivered for duokey was engineered to eliminate systemic bottlenecks, reduce infrastructure spending, and accelerate business throughput without vendor lock-in.
| Architectural Metric | Pre-Existing Legacy Monolith | Generic Solution Engine |
|---|---|---|
| Cloud Adoption Status | Completely blocked by FINMA regulators | 100% regulatory approval for multi-cloud data vaults |
| Cryptographic Key Rotation | 45-day manual security ceremony | Automated zero-downtime daily rotation (< 100ms) |
| Hypervisor Compromise Defense | Plaintext keys vulnerable in VM RAM | Mathematically impossible key reconstruction |
| Quantum Cryptanalysis Readiness | Vulnerable legacy RSA 2048 / 4096 | Post-quantum hybrid NIST ML-KEM implemented |
100% IP Ownership
Full source code, Git history, Terraform state, and Docker containers transferred to your enterprise GitHub organization. Zero licensing fees or royalty locks.
Enterprise Security Standards
Audited for SOC-2 Type II, HIPAA BAA enclaves, and GDPR Article 32 compliance with mathematically verified cryptographic audit trails.
10-Day Production Kickoff
Senior engineering pods embedded into your Jira, Slack, and GitHub workflows within 10 days of alignment.
"DuoKey's sovereign enclave architecture engineered by Generic Solution gave our institutional banking clients the highest possible cryptographic guarantees in the industry. It allowed us to leverage hyperscale cloud without compromising Swiss banking secrecy."
Deploy an architecture like duokey for your enterprise.
We construct production software platforms with zero technical debt, 100% intellectual property transfer, and deterministic high-availability performance.